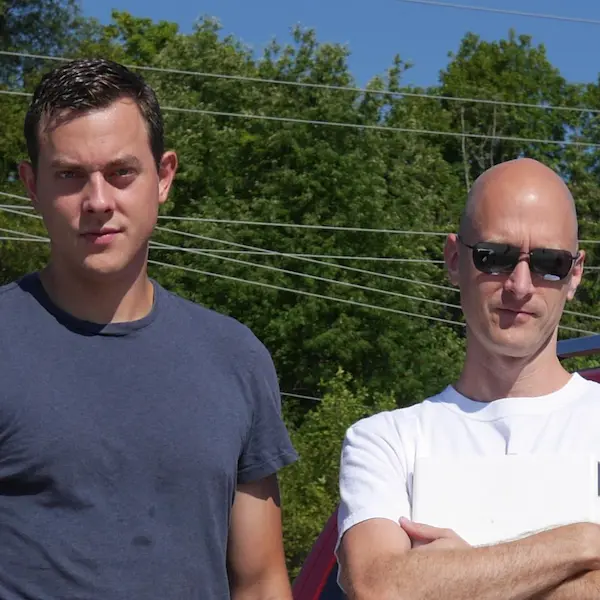
Chris Valasek & Charlie Miller
World-Renowned 'White Hat' Hackers | The Duo Behind the Famous Jeep Hack | Autonomous Vehicle & Connected Car Experts | Pioneers of Automotive Cybersecurity


Principal Autonomous Vehicle Security Architect, Cruise | Former NSA Hacker | 4x Pwn2Own Champion | Cybersecurity & IoT Expert
Few people on earth have hacked the iPhone, Android, and a moving car on a public highway. Dr. Charlie Miller has done all three. A former NSA operative and four-time Pwn2Own champion, he forced a 1.4 million-vehicle recall with a single live demonstration. His talks give senior audiences an insider view of how attackers think and where real organizational risk lives.
Want to book Charlie Miller as a speaker for your event? Please provide the info below and we’ll get in touch within 24h:
Cybersecurity speaker Charlie Miller is one of the most technically accomplished ethical hackers alive, a Ph.D. mathematician turned NSA operative whose discoveries forced Apple, Fiat Chrysler, and the wider automotive industry to rethink how they defend their systems. Named by Foreign Policy as one of the most skilled hackers in the world, Dr. Miller holds a doctorate in mathematics from the University of Notre Dame and spent five years as a computer hacker for the National Security Agency before bringing that tradecraft to the private sector.
His record of high-impact, responsible disclosure is virtually unmatched. He was the first person ever to remotely compromise an iPhone, exploiting an SMS vulnerability that allowed a complete device takeover with no user interaction, and he replicated the feat on Android. He won Pwn2Own, widely regarded as the Super Bowl of computer hacking, four times, exposing critical flaws in Apple’s Safari browser and the MacBook Air. Beyond mobile, he uncovered vulnerabilities in laptop battery firmware and NFC communications, consistently staying ahead of emerging threats.
At Wired‘s invitation, and working alongside researcher Chris Valasek, Dr. Miller demonstrated the most consequential automotive cybersecurity exploit on record: the remote takeover of a 2014 Jeep Cherokee through its cellular-connected infotainment system, with a journalist at the wheel on a St. Louis highway. From ten miles away, and without ever touching the vehicle, the pair controlled steering, braking, and acceleration. The disclosure forced Fiat Chrysler to recall 1.4 million vehicles and drew new federal attention to automotive cybersecurity standards. It remains the moment that elevated vehicle hacking from theoretical concern to urgent industry priority.
Dr. Miller has applied that expertise at Twitter, Uber’s Advanced Technology Group, Didi Chuxing, and Cruise, General Motors’ autonomous vehicle unit, where he serves as Principal Autonomous Vehicle Security Architect. His work has been covered by ABC World News Tonight, The Today Show, NPR, CNN, the New York Times, CNBC, USA Today, and Forbes. He is also co-author of The iOS Hacker’s Handbook, a definitive technical guide to Apple platform vulnerability research.
As a speaker, Charlie Miller translates deeply technical material into urgent, practical insight for boards, executive teams, and security leaders. His presentations take audiences inside the mind of an attacker, showing not only how breaches happen but why organizations systematically underestimate their risk. Whether the subject is enterprise network defense, connected vehicle security, IoT vulnerabilities, or the convergence of AI and cyber risk, his talks are grounded in real exploits he personally executed, making the danger concrete. Senior audiences leave with a sharper sense of where their exposure lies and which changes matter most.
Most security programs are built around compliance checklists rather than the reality of how skilled attackers operate. Drawing on his own landmark exploits, Dr. Miller walks audiences through the attacker mindset: how vulnerabilities get discovered, how systems are mapped, and how organizations repeatedly leave the same categories of exposure unaddressed. Attendees come away with a clearer view of where their risk actually lives and which defenses genuinely move the needle.
The vehicle that proved a car could be hijacked from ten miles away was not a prototype; it was a production model on a public road. Using the famous Jeep Cherokee exploit and his work as a security architect for autonomous vehicles, Dr. Miller examines what secure connected-vehicle design looks like, why legacy automotive architecture creates systemic risk, and what the industry must solve before autonomy scales. Essential for automotive, transportation, logistics, and smart-infrastructure audiences.
Enterprise networks are defended by people who have rarely tried to break into them. Charlie Miller has spent decades doing exactly that, across mobile devices, embedded systems, and complex connected infrastructure. In this session he walks audiences through the reconnaissance, pivot, and exploitation techniques attackers use against real enterprise environments, translating each step into concrete defensive priorities. The result is a conversation that speaks to the CISO and the board alike.
The spread of connected devices, from factory floors to smart buildings to consumer electronics, has dramatically widened the attack surface available to adversaries. Dr. Miller examines how IoT and AI-enabled systems introduce new classes of vulnerability, how attackers already exploit them, and what organizations should prioritize as their environments grow more interconnected. A forward-looking session for technology, operations, and executive leadership teams working through digital transformation.
World-Renowned 'White Hat' Hackers | The Duo Behind the Famous Jeep Hack | Autonomous Vehicle & Connected Car Experts | Pioneers of Automotive Cybersecurity

MythBusters Co-Host & Executive Producer | NYT Bestselling Author | Board Member, Smithsonian Air & Space Museum | Innovation & Creativity
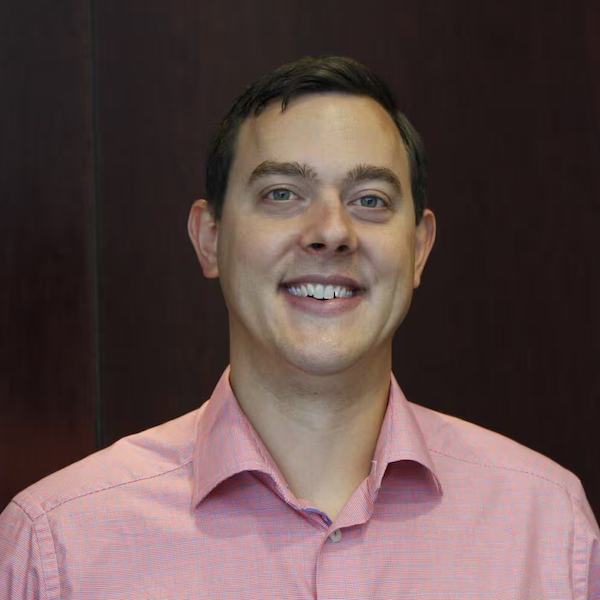
Director of Product Security at Cruise (GM) | Famed Jeep Hacker | Autonomous Vehicle & IoT Cybersecurity Expert | DEF CON & Black Hat Speaker


© 2026 Aurum Speakers Bureau. All Rights Reserved
| Basic Data Protection Information | |
|---|---|
| Data controller | AURUM SPEAKERS BUREAU S.L. |
| Address | Parc Audiovisual de Catalunya 1, Oficina S11, 08225 Terrassa, Spain |
| Purposes | We will use your data to respond to your requests and deliver our services to you. |
| Marketing | We will only send you marketing correspondence if you have given your prior consent, which you can do by ticking the box for that purpose. |
| Lawful basis | We will only process your data if you have given your prior consent, which you can do by ticking the box for that purpose. |
| Recipients | Generally, only our members of staff who have been duly authorised may access the data that you have provided. |
| Your Rights | You have the right to know what information we hold about you, to rectify it and to erase it, as explained in the additional information available on our website. |
| Additional Information | For more information, please see our "PRIVACY POLICY". |